Bot website guests is steadily framed as a security problem or an SEO problem. Then again on WordPress internet hosting infrastructure, it presentations up as a potency problem, in particular one concentrated in a very particular set of URLs.
No longer all requests rate the an identical. The difference between a cached static internet web page and a dynamic endpoint isn’t a slight potency nuance. It’s the difference between a request that costs just about no longer anything else and one who reserves a PHP thread, triggers an entire database query, and generates session overhead, without reference to whether or not or no longer the client is a real purchaser or a bot that certainly not converts.
Working out why some endpoints are far more dear than others is what separates a bot regulate methodology that if truth be told works from one who blocks a substantial amount of or too little.
No longer all requests are similar
When a buyer lands on an ordinary WordPress internet web page, similar to a blog submit, a product file, or an “about” internet web page, the server just about always serves that response from cache.
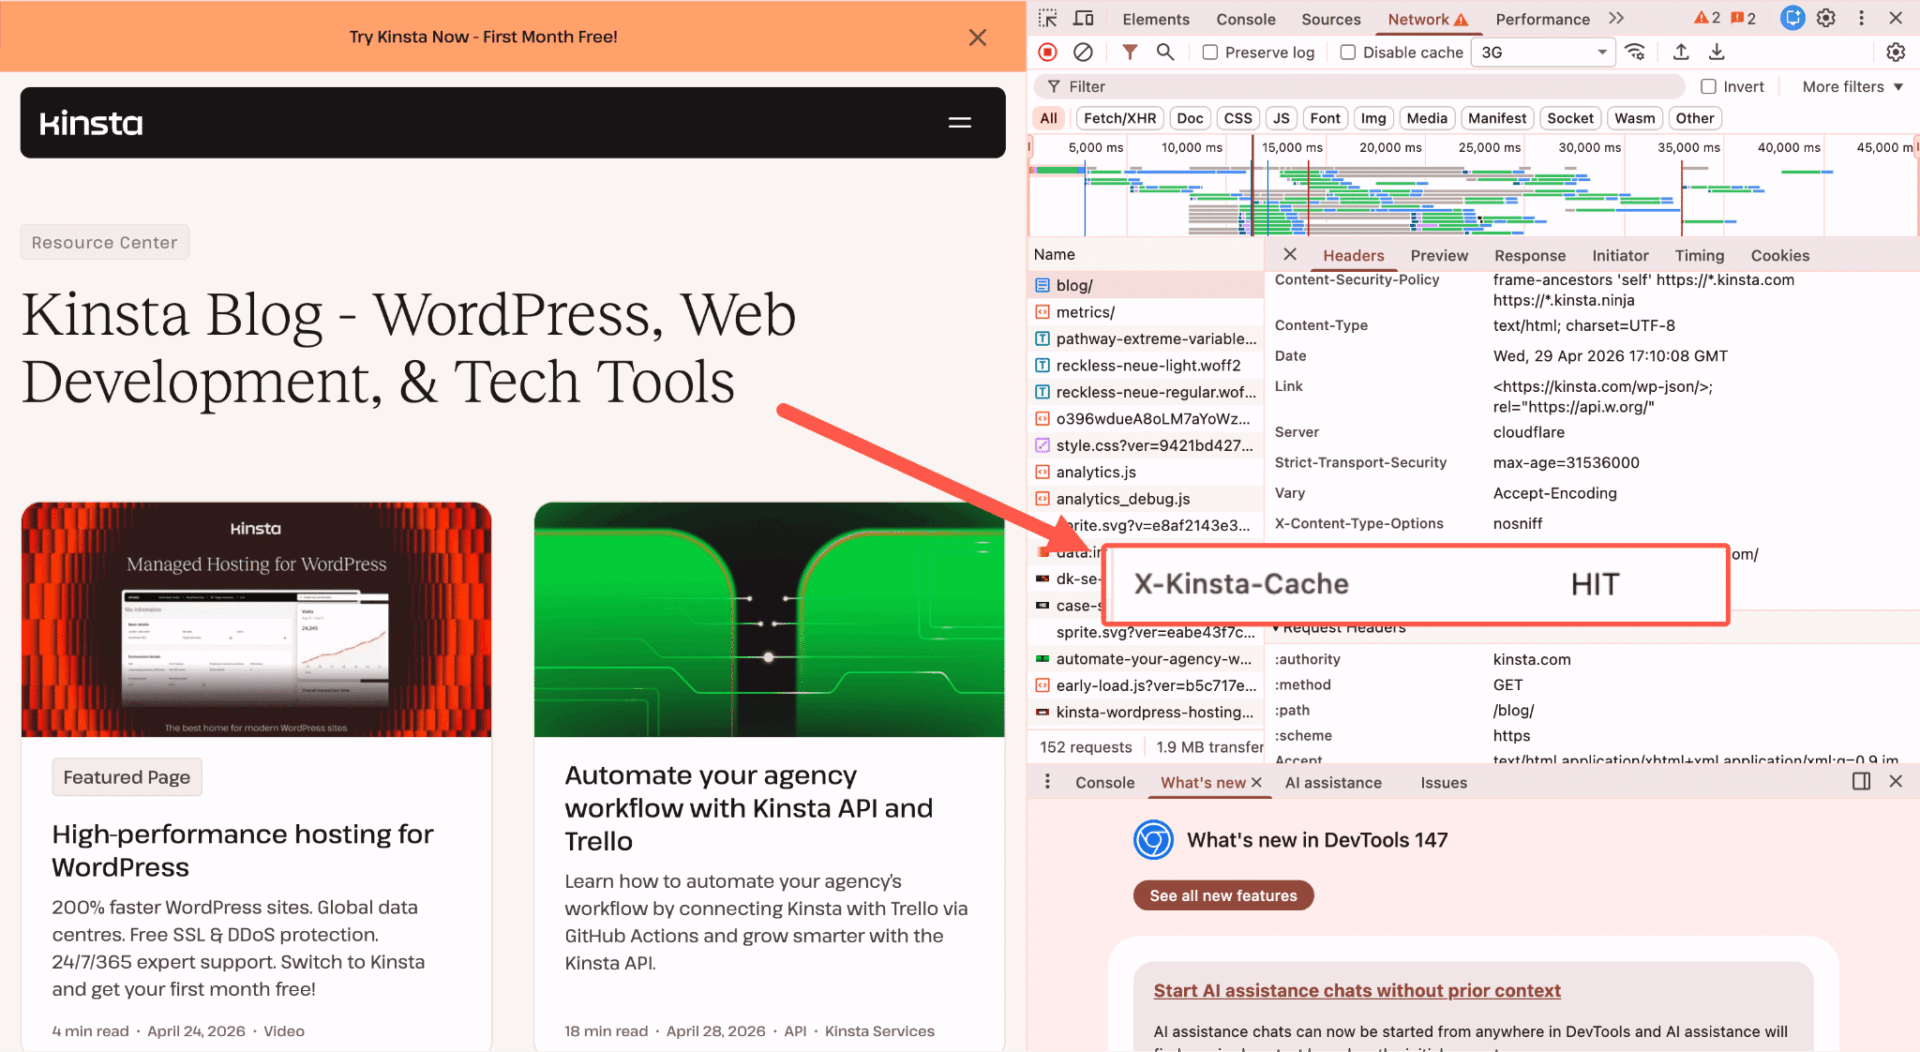
Kinsta’s full-page cache handles this at the edge, so the request certainly not triggers a server’s PHP or its database.
But when a request lands on a non-cacheable endpoint, the server has to do exact artwork. A PHP thread is allocated and held for the entire period of the request, and your database is queried. If the internet web page involves cart state, client categories, or custom designed content material subject matter, session coping with supplies each different layer. None of this may also be cached, given that response is unique to each request.

On a healthy web page with maximum often human visitors, this is implausible. Your dynamic endpoints serve exact customers who add items to their cart, check out, and search for products. The load is proportional to express usage.
Bot website guests breaks this taste. A crawler doesn’t add to the cart or convert, on the other hand it triggers the an identical server-side execution as a real purchaser would, at a charge no human might deal with.
The best endpoints where this bites
On a WooCommerce retailer, the following URL patterns and endpoints are non-cacheable by means of design, they usually’re exactly those who bot website guests tends to hit hardest.
?add-to-cart=
This is necessarily probably the most resource-intensive example we documented in our AI & bot site visitors record. Together with a product to the cart requires PHP execution, a database write, and session creation or validation. There’s no cached fashion of this response, as each hit is contemporary artwork.
To place the scale in context: Kinsta’s infrastructure data once recorded 7.67 million add-to-cart hits from 5 bots in a 24-hour window.

That’s about one request every 11 milliseconds, all day and all night, each tricky entire PHP and database execution, each generating no important output for the crawler, and none serving a purchaser.
/cart and /checkout
The ones pages are excluded from internet web page cache by means of default in WooCommerce. They bring about about live session data, custom designed cart state, and (when it comes to checkout) charge processing commonplace sense.
A bot hitting /checkout repeatedly isn’t doing the remaining useful, on the other hand the server doesn’t know that. It processes every request as despite the fact that it’s generally a exact transaction.
?s= (Search queries)
WordPress and WooCommerce search queries run in opposition on your database on every request. There’s no cache layer that can soak up a novel search string.
A crawler running via parameterized URL permutations or simply following every search link it finds can generate a longer tail of unique, dear database queries.
That’s the position the problem compounds. A normal WooCommerce product catalog generates URLs like:
/retailer/?color=blue
/retailer/?color=blue&measurement=M
/retailer/?color=blue&measurement=M&orderby=value
/retailer/?color=blue&measurement=M&orderby=value&paged=2
To a human, the ones are minor permutations on the an identical internet web page. To a bot following links, each one is a novel URL worth crawling, and each one requires the server to execute a filtered database query from scratch.
Google’s documentation explicitly identifies faceted navigation as a provide of transfer slowly inefficiency, where crawlers uncover near-infinite permutations of the an identical content material subject matter. Then again the issue isn’t merely that this wastes transfer slowly budget. Every variation costs exact server belongings to generate.
AJAX-powered interactions
Many WordPress plugins, similar to wishlists, availability assessments, live pricing updates, and calendar views, rely on AJAX requests that bypass internet web page cache utterly.
A bot that triggers the ones interactions, even indirectly by means of loading a internet web page that fires them, creates server-side load that doesn’t show up as a “internet web page request” to your analytics on the other hand does show up to your PHP thread usage.
What happens when PHP threads run out
Every dynamic endpoint hit holds a PHP thread for all the period of that request. That component seems minor in isolation, on the other hand thread capacity is finite, and bots don’t queue in a well mannered way.
Kinsta allocates a collection collection of PHP threads in keeping with WordPress web page, and each non-cached request reserves one for its period.
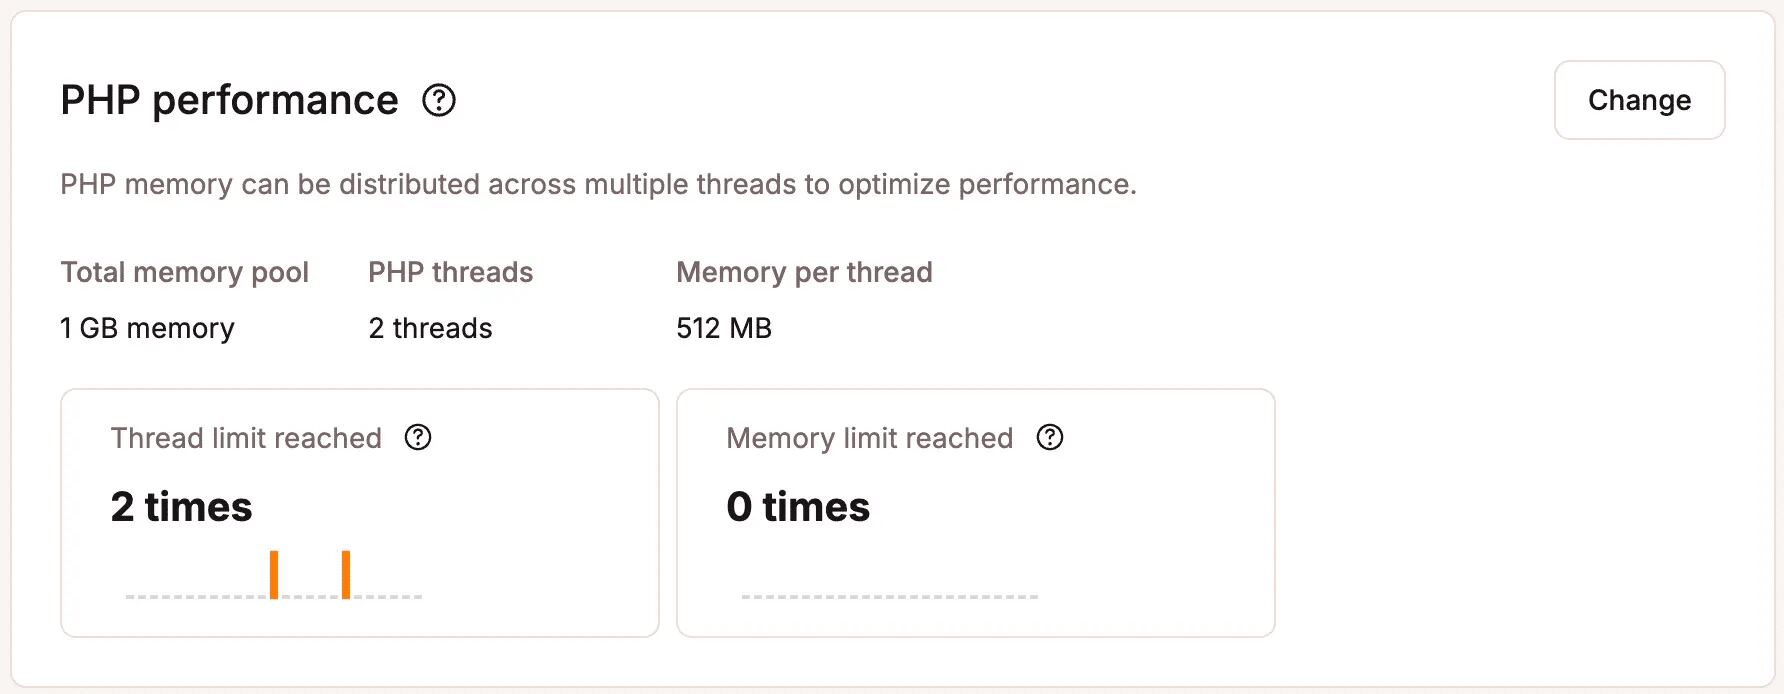
Underneath same old website guests, this is rarely a constraint. Requests are to be had, get processed briefly, and threads liberate.
Underneath sustained bot load on dynamic endpoints, threads get reserved and held. When all threads are occupied, new incoming requests wait in a queue. Exact customers if truth be told attempting so that you could upload a product to their cart or whole a checkout experience gradual internet web page quite a bit, timeouts, or HTTP 504 mistakes.

That’s the infrastructural reality that makes bot website guests on dynamic endpoints materially different from bot website guests on cacheable pages.
The loop problem: When bots get stuck
Numerous the bot website guests Kinsta’s infrastructure workforce sees isn’t the result of an intentional attack. It’s the result of crawlers following every link on every internet web page without any mechanism to recognize when they’re getting into into circles.
Proper right here’s what a query-string loop looks like in practice:
- A bot arrives at
/retailer/ - The internet web page comprises a link to
/retailer/?color=blue(a filtered view) - That internet web page comprises a link to
/retailer/?color=blue&measurement=M - That internet web page comprises a link to
/retailer/?color=blue&measurement=M&orderby=value - That internet web page comprises a link so that you could upload something to cart:
/retailer/?add-to-cart=123 - Every of the ones generates relatively different links that the bot hasn’t visited however
The bot follows everyone. It has no considered “I’ve already seen this product internet web page in a distinct filter state.” Every URL seems to be like new, gets requested, and hits the server contemporary.
This exact building of bots traversing query string permutations all through dynamic endpoints is without doubt one of the most not unusual problems we well-known in our file. A single loop rule precipitated by means of one misbehaving building filtered 550 million requests in 30 days on Kinsta’s infrastructure. That isn’t an attack, on the other hand inefficient automation at scale, compounding because of no longer anything else caught it early.
What good bot regulate looks like at the endpoint level
For WooCommerce shops and WordPress web sites with dynamic capacity, a few concepts hold without reference to your particular setup.
- Robots.txt is an indication, not a protect. You’ll (and will have to) disallow crawlers from
/cart,/checkout, and?add-to-cart=paths to yourrobots.txt. Googlebot respects this. On the other hand,robots.txtcompliance is voluntary. A emerging proportion of AI training crawlers each don’t take a look at it or don’t honor it. Disallowing a path inrobots.txtcommunicates your intent; enforcing it requires a WAF-level rule. - Tighten up URL parameter generation. WooCommerce’s default configuration generates a longer tail of URL variants via session tokens, quantity parameters, and filter mixtures. Decreasing parameter sprawl at the provide via canonical tags, consolidated permalink structures, and robots.txt
Disallowregulations on parameter variants provides crawlers fewer loops to get stuck in. - Monitor at the endpoint level, not merely total request amount. A spike in overall website guests is usually a advertising marketing campaign. A spike in requests to
?add-to-cart=from a non-browser client agent is a bot problem. Server logs and analytics equipment that show you request distribution by means of URL building and client agent are the difference between catching this in hours and catching it in days. - Offer protection to PHP thread capacity as a primary metric. If your PHP threads are continuously running at capacity and likewise you don’t have a corresponding spike in exact client categories, bot website guests on dynamic endpoints is kind of definitely a contributing factor. Kinsta’s APM tool surfaces the slowest PHP transactions by means of endpoint, so if cart or checkout paths are the culprit, you understand it immediately fairly than guessing.
What this looks like for quite a lot of web page types
The dynamic endpoint problem is most acute for WooCommerce shops, on the other hand it seems that all through different web page types in quite a lot of bureaucracy.
- WooCommerce shops face the most productive imaginable probability because of their most costly endpoints, like cart, checkout, and filtered product pages, are exactly the ones bots generally tend to hunt out via same old link-following. The results are direct: PHP thread exhaustion in every single place bot spikes degrades checkout potency for exact customers.
- Content material subject matter web sites and blogs are a lot much less exposed on the checkout side, on the other hand may also be significantly affected by bots traversing paginated archives, tag pages, and search results. Every unique search query is a up to date database hit. An aggressive crawler running via a large archive systematically can generate a sustained database load even without touching any “store” capacity.
- Trade and services and products and merchandise web sites are further exposed on form endpoints (contact bureaucracy, quote request bureaucracy, and booking flows), which include session coping with and steadily database writes. Bot-submitted form data is a distinct kind of problem (CRM air air pollution, wasted product sales effort), on the other hand the underlying mechanism is similar: dynamic endpoints that rate exact belongings on every hit.
- Web apps and SaaS products are necessarily probably the most refined case. Their API endpoints, dashboard routes, and application commonplace sense are utterly non-cacheable, and any bot website guests that reaches the application layer bypasses caching infrastructure utterly. The proper response that is maximum continuously a difficult block on all non-authenticated website guests to
/apiand/apppaths, with explicit allowlisting for first rate integrations.
Going deeper: The entire symbol on bot website guests
The dynamic endpoint problem is one part of a broader shift in how bot website guests affects WordPress infrastructure. AI crawlers have grown significantly in amount and changed in conduct, further aggressive link-following, further willingness to omit about transfer slowly directives, and further website guests hitting precisely the endpoints that rate necessarily probably the most to serve.
For a whole check out what’s changed, the data at the back of it, and a framework for making bot regulate alternatives in keeping with your particular web page kind and priorities, Kinsta’s entire file on The AI & Bot Site visitors Truth Test covers all of it, at the side of analysis all through more than 10 billion requests on Kinsta-managed infrastructure.
For many who’re able to act on what you’ve be told proper right here, Kinsta’s Bot Coverage handles the commonest patterns robotically, at the side of protection for high-cost dynamic endpoints. Allow your desired level of protection once in MyKinsta, and the machine manages the remainder.
You’ll moreover achieve out to the support workforce if you want to have explanation.
The submit Why dynamic endpoints are the most costly a part of bot site visitors appeared first on Kinsta®.
0 Comments