You migrate a web site, everything seems to be like fine for your end, and then the messages get began coming in. Some visitors see the new internet website, others are nevertheless hitting the out of date one, and a few document errors you’ll’t reproduce the least bit.
When that happens, it’s easy responsible the host or the migration itself. Further regularly than not, though, the actual purpose is DNS (not because it’s broken, alternatively because it’s doing exactly what it’s designed to do).
DNS updates don’t happen swiftly. They rely on layers of caching and resolvers outside your website hosting surroundings, which is why migrations can actually really feel unpredictable even supposing the internet website is ready.
This knowledge explains what DNS if truth be told controls, why propagation behaves another way for more than a few folks, and how to plan a migration so DNS is a controlled final step instead of a provide of downtime or confusion.
What DNS if truth be told does
DNS answers an overly particular question: Where must this house point?
When somebody enters your house in a browser, DNS translates that determine into an IP deal with. That IP cope with tells the browser which server to connect to. DNS doesn’t load pages or care what’s operating on the server. It merely handles the glance up.
To make that glance up art work reliably, DNS is broken into a few separate pieces, each and every with a clear serve as.
- House registrar: Your registrar is where the realm is purchased and renewed. It doesn’t host your internet website or control website guests. From a DNS perspective, its number one responsibility is pointing the realm to the right kind nameservers.
- Authoritative DNS provider: That’s the supplier that stores your DNS data and offers the overall answer when the internet asks where your house must get to the bottom of. Providers like Cloudflare or your webhosting platform regularly serve this serve as.
- Nameservers: Nameservers tell the internet which DNS provider is authoritative for your house. They don’t come with site knowledge or configuration themselves. They simply route DNS queries to the fitting place.
- DNS information (A, AAAA, CNAME): The ones information define where website guests goes. A knowledge point a web site to an IPv4 deal with, AAAA information point to an IPv6 cope with, and CNAME information alias one house to each and every different.
Together, the ones information decide which server visitors reach when they load your internet website.
Merely as crucial is what DNS does not do. DNS doesn’t serve knowledge, switch databases, sync content material subject material, or arrange SSL certificate. It not at all touches your website hosting surroundings.
Once that boundary is apparent, the rest of the migration process becomes much more straight forward to reason about.
What changes all over a internet website migration and what stays the equivalent
One reason DNS causes this kind of lot confusion all over migrations is that only a small part of the setup if truth be told changes. The rest stays exactly as it was once quicker than, although the internet website itself could also be moving to an entirely new surroundings.
All over an ordinary internet website migration, a few problems maximum frequently trade.
- The IP cope with nearly always changes given that internet website now lives on a unique server. This is the most common DNS-related exchange and the one that after all tells website guests where to transport.
- The website hosting surroundings changes as smartly. That includes the server, infrastructure, and platform operating your internet website. While this affects potency and stability, it’s minimize free DNS and must be completely ready quicker than any DNS updates happen.
- In a number of circumstances, particular DNS information trade. A knowledge or AAAA information are up-to-the-minute to signify to the new IP deal with. Each and every so frequently CNAME information are adjusted instead, depending on how the internet website is configured.
At the similar time, a lot of problems maximum frequently stay the equivalent.
- The area identify doesn’t trade. Visitors nevertheless kind the equivalent URL, and now not the rest regarding the public-facing deal with will have to be up-to-the-minute.
- The nameservers moreover stay the equivalent till you’re intentionally switching DNS providers. Most migrations don’t require a nameserver trade the least bit, even supposing the website hosting provider changes.
For this reason DNS is just about always the rest step in a migration. You assemble and take a look at the new surroundings first, then exchange DNS as quickly because the entirety is in a position to download website guests.
Treating DNS as a final switch instead of an early process reduces uncertainty, limits exposure, and makes downtime a long way easier to steer clear of.
DNS propagation and why it’s unpredictable
DNS propagation doesn’t suggest the internet is “updating” your house swiftly. It describes how long it takes for DNS changes to be picked up, cached, and reused all the way through many impartial strategies.
When somebody visits your internet website, their request doesn’t transfer in an instant to your DNS provider each time. It maximum frequently passes via a recursive resolver, regularly operated by the use of an ISP, an organization group, or a public supplier like Google or Cloudflare. That resolver asks the authoritative DNS provider for an answer, then stores the result for later use.
Once a resolver caches a DNS response, it keeps the use of that answer until the cache expires. That’s the position unpredictability is to be had in. Different resolvers cache DNS knowledge for more than a few lengths of time. Some respect TTL values precisely. Others follow their own limits or reuse cached information longer than expected.
Additionally, browser and dealing machine caches can store DNS results locally. Despite the fact that the global DNS document has been up-to-the-minute, an individual’s software would possibly continue to use an older answer until the local cache clears or expires.
This layered caching explains why two folks in different puts can see different diversifications of the equivalent internet website at the similar time. One resolver has the new IP deal with. Another continues to be pointing to the out of date server.
The standard “24-48 hours” rule oversimplifies what’s in truth happening. Many purchasers see updates in minutes. Others received’t see them for for for much longer, depending on how their resolver and local caches behave.
TTL and the best way it’s serving to steer clear of downtime
TTL, or Time to Live, controls how long DNS answers are cached quicker than a resolver asks for modern wisdom. It doesn’t drive updates to happen sooner, nevertheless it no doubt limits how long out of date wisdom will also be reused.
Every DNS document has its private TTL worth, measured in seconds. If a document has a TTL of 300, resolvers would possibly reuse that answer for up to 5 minutes quicker than checking over again. A TTL of 86,400 allows caching for an entire day.
For this reason lowering TTL quicker than a migration problems. If resolvers are already maintaining short-lived DNS answers, they refresh additional perpetually when you trade information. That reduces the window where visitors could be sent to the out of date server after the switch.
For lots of migrations, a TTL between 300 and 600 seconds strikes a very good balance. It’s fast enough to limit propagation delays without striking pointless load on DNS infrastructure.
Going too low would possibly purpose problems. Extremely fast TTLs don’t be sure that rapid updates, and a couple of resolvers put out of your mind about surprisingly small values. Others would possibly rate-limit requests or fall once more to cached knowledge anyway. Lowering TTL at the closing minute is each and every different now not peculiar mistake. If caches already dangle long-lived information, changing the TTL received’t have an effect on them until those caches expire.
Probably the most protected approach is timing. Scale back TTL a minimum of 24 hours quicker than the migration, confirm the new worth is live, and highest then schedule the DNS trade.
A safe DNS migration timeline (step by step)
A simple DNS migration prioritizes sequencing over tempo. When each and every step happens in the fitting order, DNS turns right into a controlled switch instead of a guessing sport. Proper right here’s how to transfer about it successfully:
1. Get able the new website hosting surroundings
Organize the new internet website totally quicker than touching DNS. That includes putting in place dependencies, configuring caching, putting in redirects, and verifying potency.
Check out the internet website the use of a temporary URL or a space hosts file so that you’ll view it as despite the fact that DNS already problems to the new server. Make certain that SSL certificates are ready and legit, in particular if HTTPS is enforced. DNS must not at all be the step where you in finding configuration issues.
You’ll modify DNS knowledge within MyKinsta merely by the use of going to your dashboard, clicking DNS then Add your first house determine.

2. Lower TTL prematurely
Scale back TTL values on linked DNS information smartly ahead of the migration. Ideally, do this a minimum of 24 hours quicker than the planned switch.
After changing TTL, confirm the new worth is live the use of DNS glance up tools. This promises resolvers get started caching shorter-lived answers quicker than any IP changes happen.
3. Freeze bad changes
Pause content material subject material edits, e-commerce orders, and form submissions if the internet website depends on a single database. DNS doesn’t switch knowledge, so changes made to the out of date internet website after the migration snapshot will also be out of place.
Most migration knowledge issues come from overlapping writes, not DNS delays. Freezing changes eliminates that opportunity.
4. Change DNS information
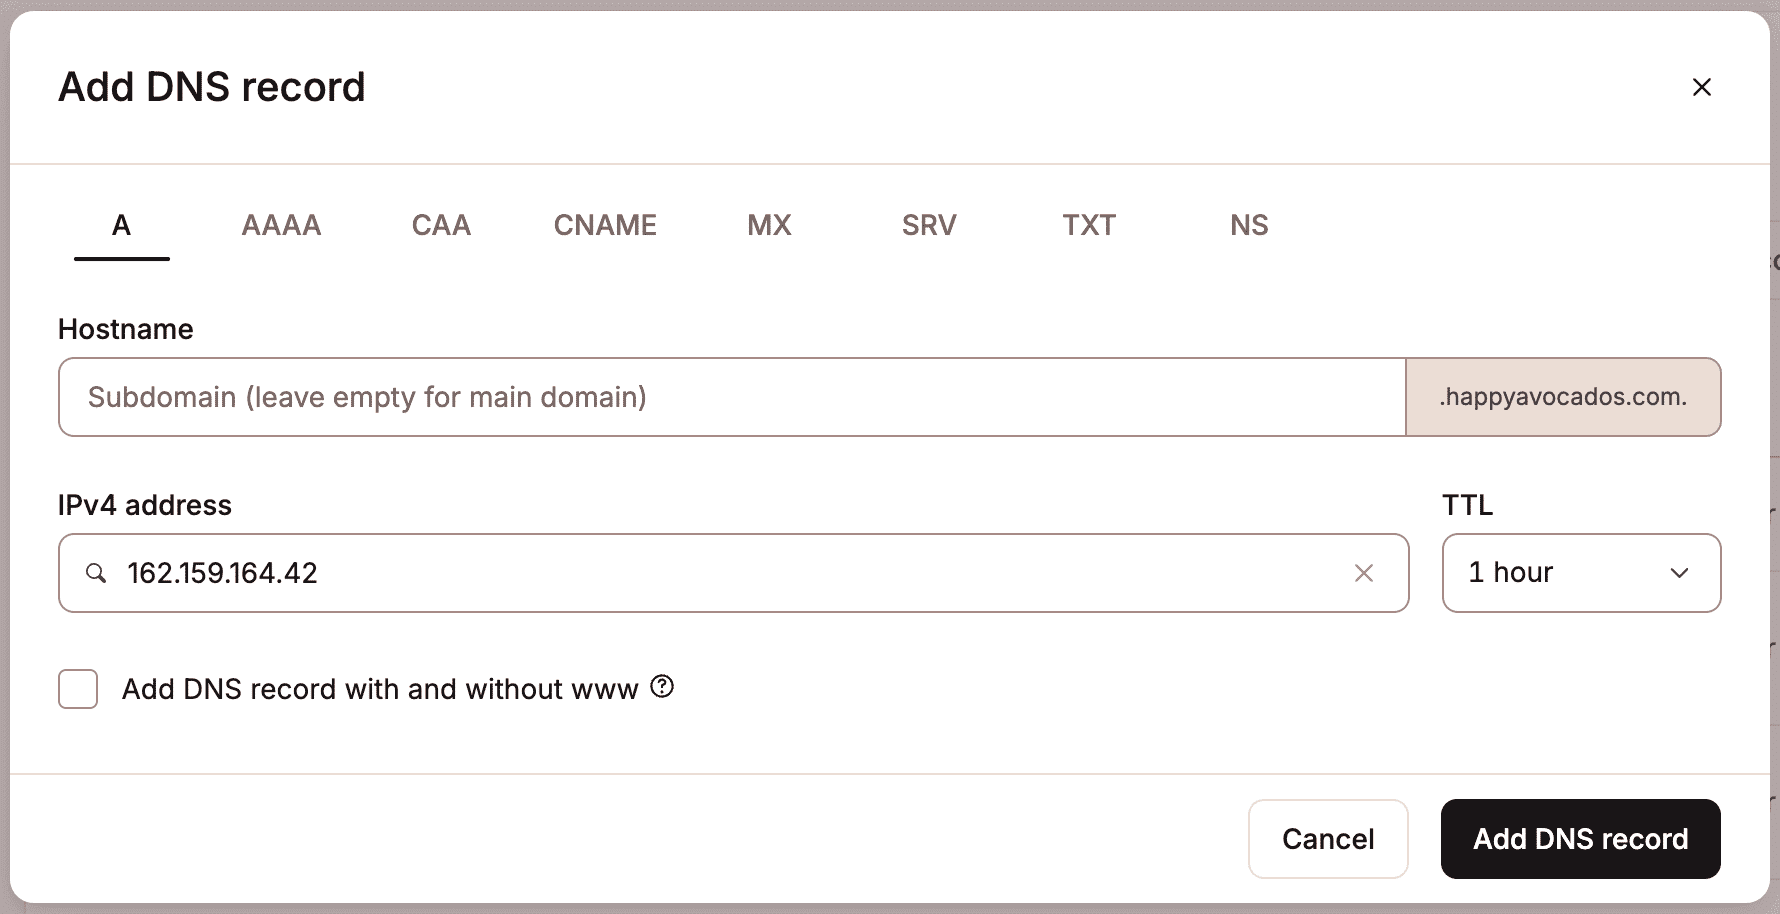
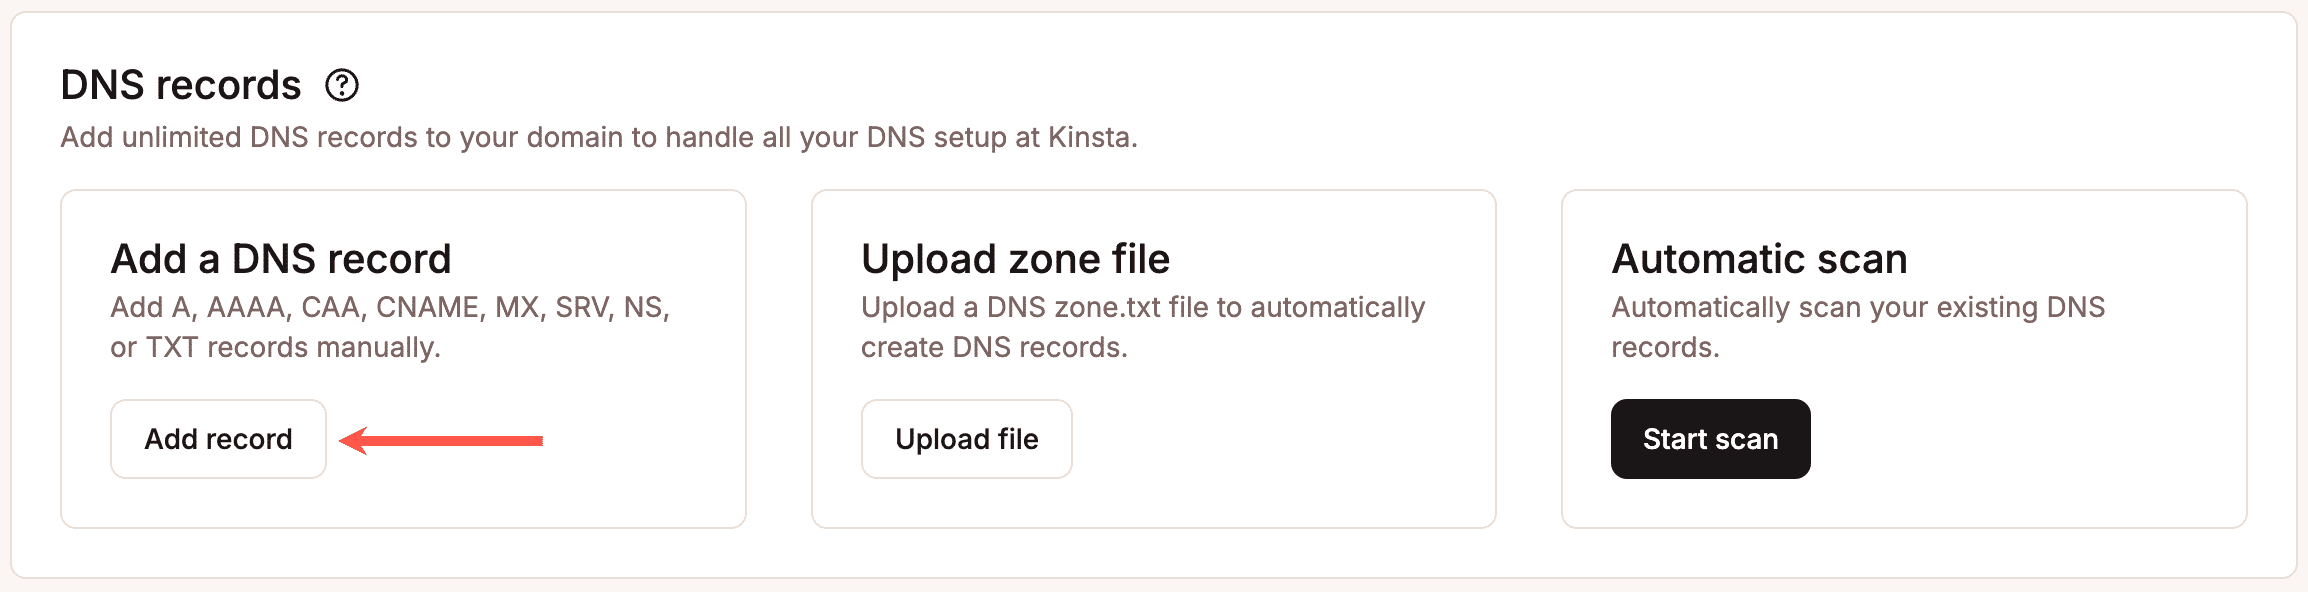
Trade highest the knowledge that need updating, maximum frequently A, AAAA, or CNAME information pointing to the internet website. Keep away from enhancing unrelated information all over the equivalent window. You’ll adjust this data within MyKinsta, too. Throughout the equivalent DNS internet web page as quicker than, scroll proper right down to DNS information and make a choice Add a DNS document so that you could upload this data manually.
Double-check IP addresses, document types, and hostnames to prevent conflicts. Once up-to-the-minute, take a look at changes the use of direct DNS queries moderately than browser testing on my own.
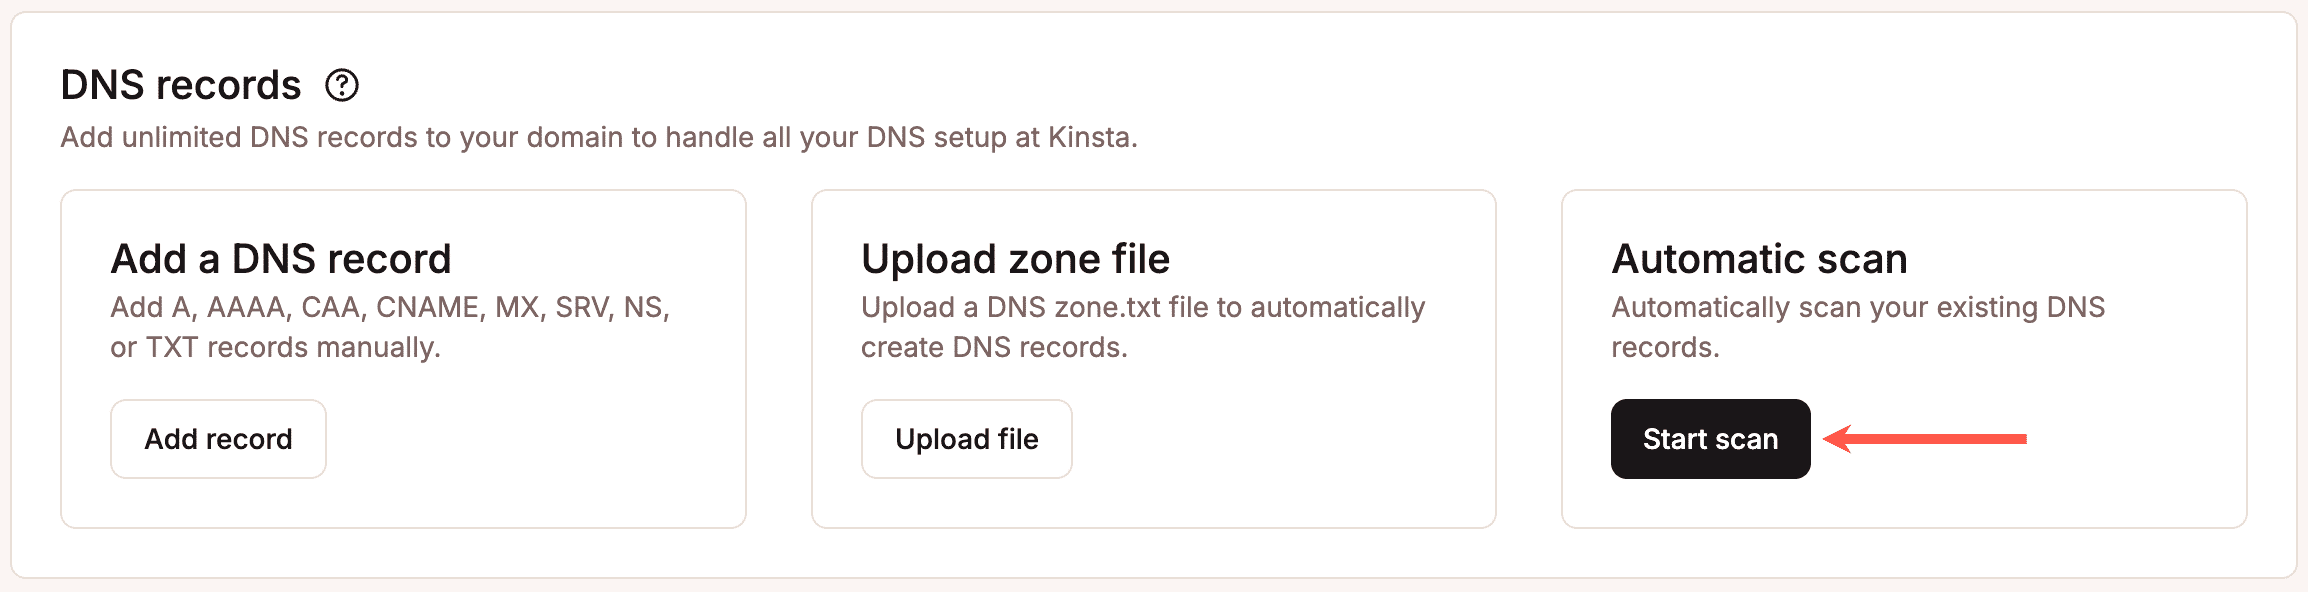
You’ll moreover habits an automatic scan of DNS information by the use of clicking Get began scan beneath Automated scan.
5. Follow propagation in precise time
Observe DNS resolution from a couple of spaces to make sure website guests is reaching the new server. Expect blended results all over rollout. That’s same old.
Excellent fortune doesn’t suggest everyone updates right away. It means new website guests repeatedly resolves to the right kind holiday spot, without errors or interruptions.
Following this assortment keeps DNS predictable. Every step limits likelihood, narrows uncertainty, and prevents downtime resulted in by the use of rushed or overlapping changes.
Where downtime maximum frequently comes from and how to prevent it
When downtime happens all over a migration, DNS regularly gets the blame. In observe, the basis purpose is maximum frequently elsewhere.
DNS issues tend to be simple and binary: a document problems to the fitting place or it doesn’t. Most outages come from gaps between DNS, website hosting, and the appliance itself.
- One now not peculiar failure point is an wrong IP deal with. A single typo or out of date worth sends website guests to the wrong server, which seems like downtime although DNS is resolving accurately.
- Missing or incomplete DNS information purpose similar indicators. Mail information, www subdomains, or verification information are from time to time overlooked all over changes, leading to partial outages or broken capacity.
- SSL misalignment is each and every different not unusual purpose. DNS would possibly point to the new server, alternatively the certificate isn’t installed or doesn’t cover the right kind house however. Browsers then block get admission to, which consumers experience as downtime.
- Caching can also art work in opposition to you. Cached content material subject material or redirects would possibly nevertheless point to the out of date server after DNS updates, in particular if reverse proxies or CDN layers aren’t aligned with the new surroundings.
Necessarily essentially the most loyal way to prevent the ones issues is overlap. Keep the out of date and new environments live at the similar time, completely helpful, until website guests has clearly shifted. When every servers can serve requests safely, DNS propagation becomes a long way a lot much less bad.
Controlled webhosting can reduce migration likelihood by the use of ensuring the new surroundings is actually able quicker than DNS changes. Most managed platforms provide staging or transient URLs, preconfigured server stacks, and SSL readiness checks, so the new internet website will also be tested end-to-end while the out of date internet website nevertheless serves visitors.
Migration beef up moreover plays a task. Professional teams validate DNS information, confirm IP assignments, and look ahead to now not peculiar misconfigurations that purpose outages. Instead of guessing whether or not or now not a topic is DNS, SSL, or application-level, problems are known and resolved earlier inside the process.
Kinsta structures migrations so that overlapping environments are the default. The out of date internet website continues serving website guests while the new internet website is able and verified. When DNS updates happen, every ends are ready to deal with requests.
DNS myths that purpose pointless panic
A lot of migration drive comes from ideas about DNS that sound inexpensive alternatively aren’t proper. Clearing the ones up makes it easier to respond lightly when problems don’t exchange right away.
“DNS changes are rapid.”
DNS updates don’t push out to the internet in precise time. They’re picked up as caches expire and resolvers refresh their knowledge. Even a wonderfully configured trade rolls out incessantly.
“If the internet website is down, DNS is broken.”
Most migration downtime isn’t resulted in by the use of DNS the least bit. SSL errors, server misconfigurations, or tool issues regularly appear as DNS disasters on account of consumers can’t load the internet website.
“Clearing cache fixes propagation.”
Clearing a browser cache would possibly have the same opinion a single particular person see the new internet website, nevertheless it no doubt doesn’t trade what resolvers or ISPs have cached. Propagation happens on their timelines, not yours.
“Changing nameservers is wanted for each migration.”
Nameserver changes are highest sought after when switching DNS providers. Most internet website migrations art work totally smartly without touching nameservers the least bit.
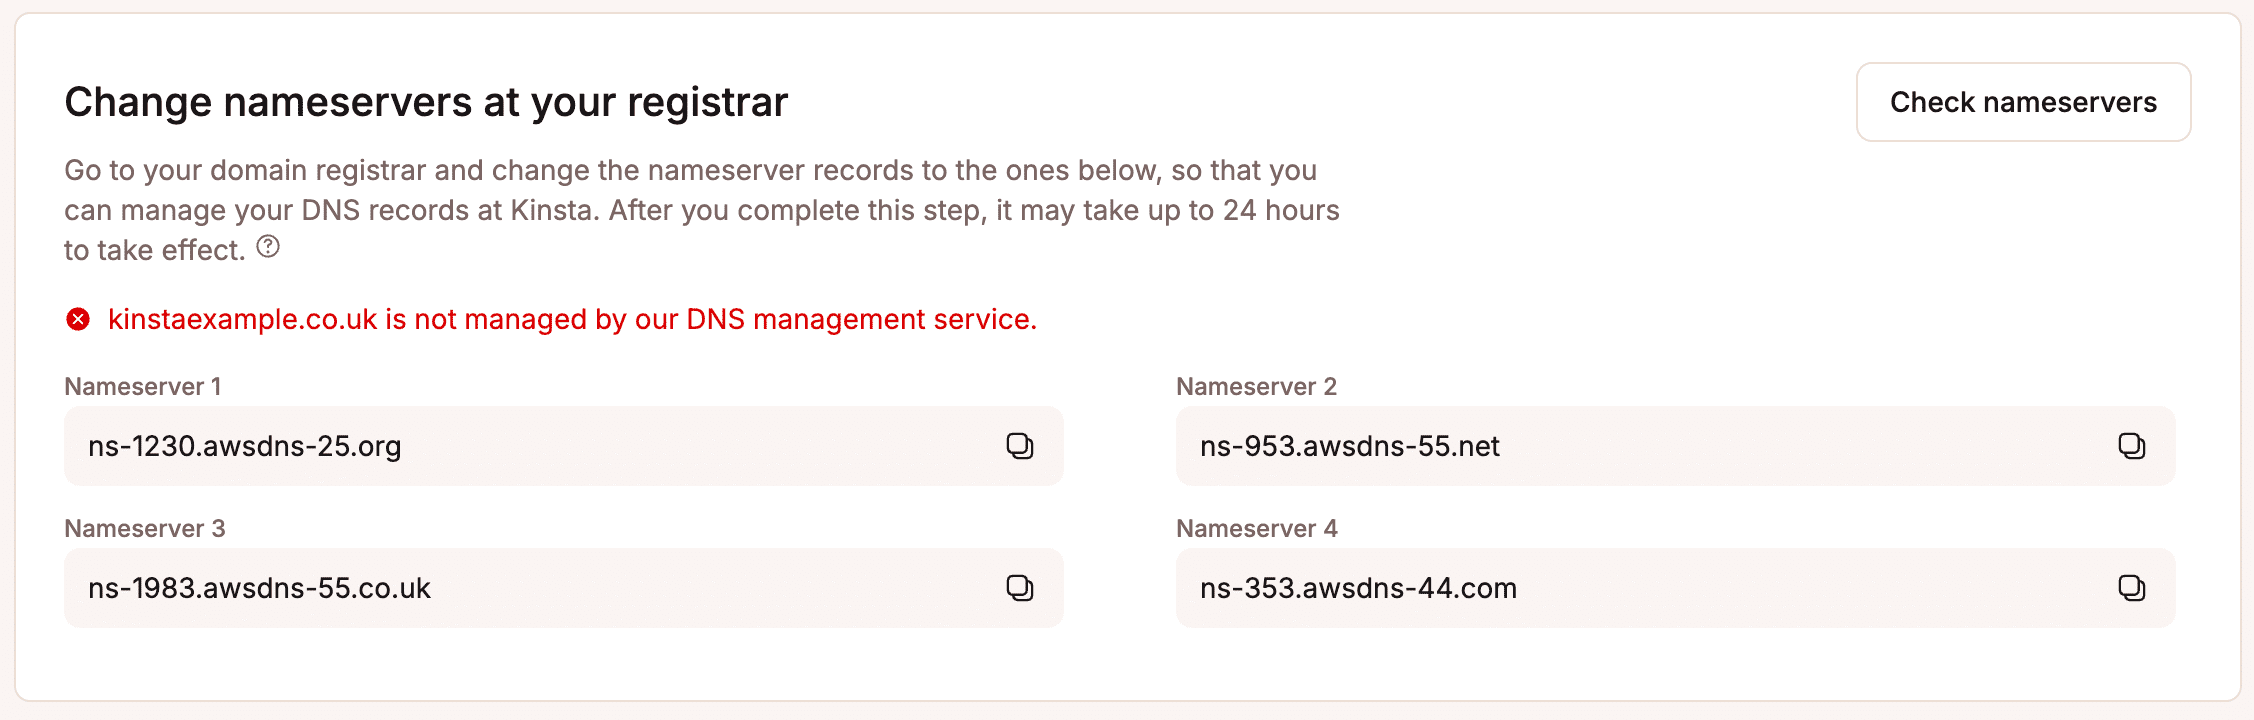
When you do need to make changes, you’ll get admission to Kinsta nameservers in MyKinsta beneath DNS> Trade nameservers at your registrar.
DNS infrequently behaves unpredictably because it’s broken. It behaves predictably in step with rules which might be easy to misunderstand. Working out those rules eliminates a large number of the panic that surrounds migrations.
Submit-migration checklist: What to do once DNS is live
Once DNS changes are in place, the art work isn’t finished. The aim now might be to make sure that website guests is constantly reaching the new surroundings and that now not the rest is quietly failing inside the background.
- Get began by the use of confirming website guests is hitting the new server: Check out server logs, analytics, or website hosting dashboards to verify requests are arriving at the right kind IP and surroundings. Mixed website guests is same old early on, nevertheless it no doubt must trend completely in opposition to the new internet website.
- Read about SSL and redirects: Make certain that certificates are reputable for all expected domains and that HTTP-to-HTTPS and legacy redirects behave as meant. Certificate errors or redirect loops regularly appear highest after precise website guests arrives.
- Follow logs and error fees: Stay up for spikes in 404s, 500 mistakes, or blocked requests. The ones indicators regularly disclose not noted configuration issues that weren’t visible all over testing.
- Once website guests has stabilized, restore same old TTL values: Longer TTLs reduce DNS query amount and fortify resolver efficiency. This step is regularly forgotten alternatively crucial for long-term stability.
- Remove legacy environments safely: Don’t shut down the out of date server until you’re confident it’s not receiving vital website guests. A short lived overlap window prevents edge-case disasters from turning into outages.
This final move turns a a good fortune DNS exchange proper right into a clean, sturdy migration.
Downtime all over migration is maximum frequently optional
Downtime all over a internet website migration is maximum frequently the result of rushed changes, overlapping tasks, or treating DNS as something that will have to be “mounted” beneath power.
Probably the most protected migrations prioritize preparation over tempo. Website online website hosting, tool configuration, and SSL are validated first. DNS is up-to-the-minute closing, with realistic expectations about propagation and caching.
With the fitting workflow and give a boost to, internet website migrations don’t need to be tense or bad. And when DNS changes occur on best of a powerful, managed surroundings, such since the controlled webhosting services and products provided by the use of Kinsta, downtime becomes an element of the former.
The submit How DNS actually works all through a web site migration (and methods to keep away from downtime) appeared first on Kinsta®.
0 Comments